Key takeaways
- Consent mode communicates a person’s choice to supported tags; it is not a consent banner or a legal determination.
- The browser still captures the choice and sends consent state even when measurement processing moves server-side.
- Basic and advanced consent mode transmit different information before consent, so the implementation choice needs documented approval.
- Test denied, granted, changed, expired, and region-specific states—not only the happy path.
01
Separate the three jobs that teams usually blur together
A consent management platform asks for and stores a person’s choice. Consent mode communicates that state to supported Google tags. A server container receives, transforms, and routes measurement requests. Buying or configuring one of these pieces does not silently complete the other two.
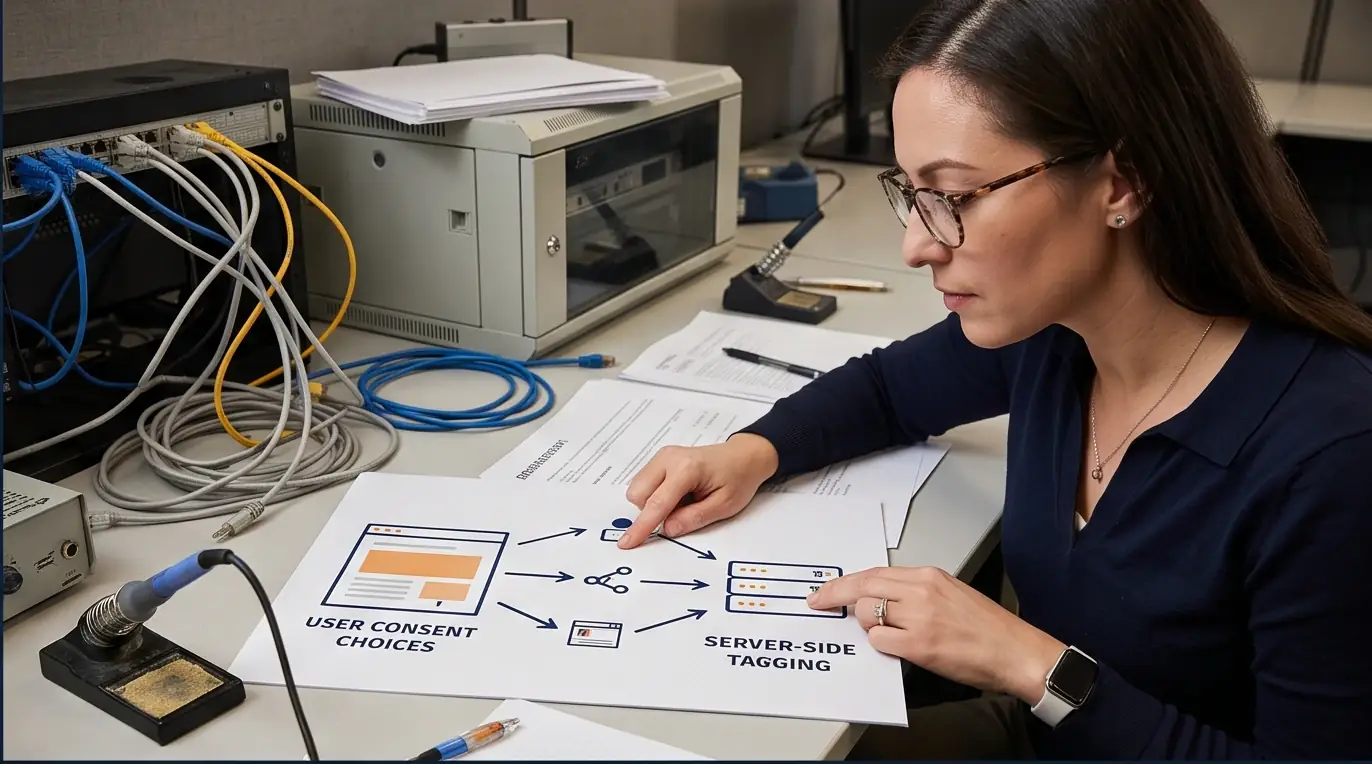
Google’s server-side consent guidance still begins in the web container: the banner updates consent, the Google tag sends those parameters, and consent-aware tags in the server container adjust their behavior. That boundary is useful because it makes the data path inspectable, but it does not decide what your organization is allowed to collect.
02
Choose basic or advanced mode with the data flow visible
In basic consent mode, Google tags are blocked until the visitor interacts and grants consent. In advanced mode, tags load with default states—commonly denied—and can send cookieless measurements before consent. Google describes the latter as supporting advertiser-specific modeling, while basic mode relies on a more general model.
Swipe to compare every column
| State | Expected browser behavior | Expected server behavior |
|---|---|---|
| Default denied | No storage for denied purposes | Only explicitly permitted or consent-aware processing |
| Granted | Permitted tags and storage activate | Route approved fields to approved destinations |
| Choice changed | Consent update is sent immediately | Subsequent requests follow the new state |
| Unknown or malformed | Fail to the documented safe default | Reject, quarantine, or minimize instead of guessing |
03
Make the server container a policy boundary
A useful server container does more than proxy the same payload. Allowlist events and fields, remove parameters destinations do not need, validate consent state, control which vendors receive which records, and log policy decisions without logging unnecessary personal data. Restrict template permissions and publishing access as carefully as production code.
Document the owner for the consent taxonomy, the tag owner, the server-container owner, and the person who approves a new destination. Without that ownership, “server-side” becomes a location change rather than a control system.
04
Test the uncomfortable states before trusting the dashboard
Run a matrix across region, device, new and returning visitors, each consent choice, withdrawal, banner failure, ad blockers, and server outage. Inspect requests at the browser, server, and destination. Reconcile a small set of known test events rather than accepting that a tag fired.
Modeling may help recover aggregate measurement gaps, but modeled events are not observed individuals. Label modeled and observed evidence correctly in reporting, and keep product, privacy, and legal review attached to the implementation rather than buried in a launch ticket.
Primary sources and further reading
Use the source material to validate details against your own context and current platform configuration.
- Google: Consent mode overview
- Google: Implement consent mode with server-side Tag Manager
- Google: Server-side tagging overview
- Google Analytics: About modeled key events
This field note follows the XenGrowth editorial policy: primary sources where available, visible limitations, material review dates, and no invented first-hand experience.
Stay with the problem